Technology Architecture
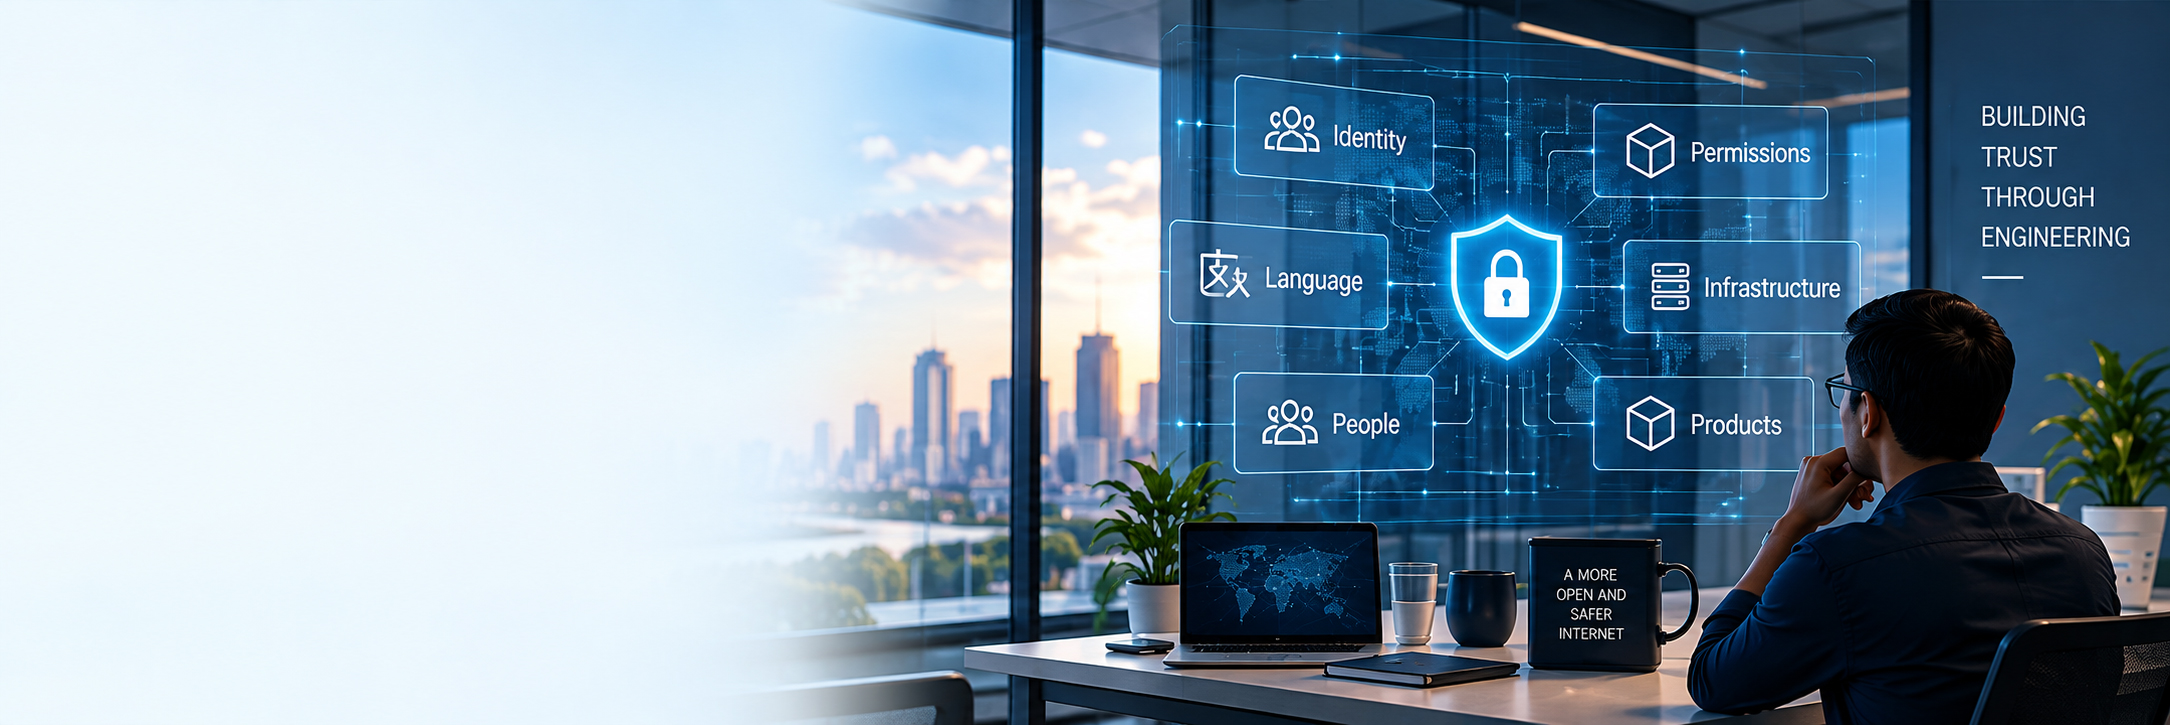
Softa’s shared engineering connects identity, permissions, language and infrastructure while preserving the authority of each product. The boundary is part of the system's not a statement added after it is built.
A shared engineering foundation with clear boundaries.
Consider an employee requesting an explanation of an authorised business document. The source system first establishes the employee’s right to access that document. The requested task identifies the material to be used. The receiving AI capability then operates within the permitted source, purpose and output conditions. Access to other documents is not inferred from the employee’s account or job title.
The boundary must remain effective in the places where information can persist: retrieval indexes, prompts, temporary caches, logs, provider services and outputs. A restriction enforced only in the visible interface would leave the architectural problem unresolved. The company’s shared-control model therefore treats permission and provenance as part of the connection.
The Softa Core Control Fabric is a shared capability layer, not an additional consumer product. The institutional baseline includes authentication primitives, policy and permission controls, localisation, notifications, media services, an AI gateway, provenance, security and key primitives, observability and portability-related capabilities.
These common functions reduce repeated engineering. They do not create shared behavioural ownership. The originating product remains responsible for its information purpose: the receiving product has a bounded task. A single infrastructure operator or senior executive does not gain unrestricted content access by virtue of position.
An integration can change risk without changing its user-facing button. A new provider may retain prompts differently; a logging change may expose content; an expanded model context may admit additional records. The architecture links such changes to source rights, access, operational evidence and a recovery path.
The release decision must distinguish a function that works from a function that preserves its information boundary. The institutional model provides specialist privacy, security, compliance and quality responsibilities alongside product ownership. It also separates internal review from an independent assessment or certification.
The company’s engineered architecture establishes the intended responsibilities and information boundaries. Product-specific notices, releases and technical records establish the implemented scope of a service. Sensitive network topology and confidential implementation details have a different disclosure purpose.
The practical purpose is clear: a useful task should be repeatable without allowing its private context to spread across unrelated products. System boundaries, human authority and recovery are evaluated together rather than reduced to an encryption label.
Clear responsibilities
Defined boundaries
People-first by design
Trust through action
OUR PURPOSE
Softa is building a connected technology ecosystem around privacy, participation and practical human needs creating digital systems designed to remain useful, responsible and inclusive as they grow.
